Authentication Policies by Service
This is a menu that allows you to manage the login authentication policies applicable to each service.
View/Search Authentication Policy
- You can check the registered authentication policies.
- You can specify a service to check the registered authentication policies for each service.
- You can check the priority of the policy, policy name, policy description, access policy settings, and the services that the policy is applied to.
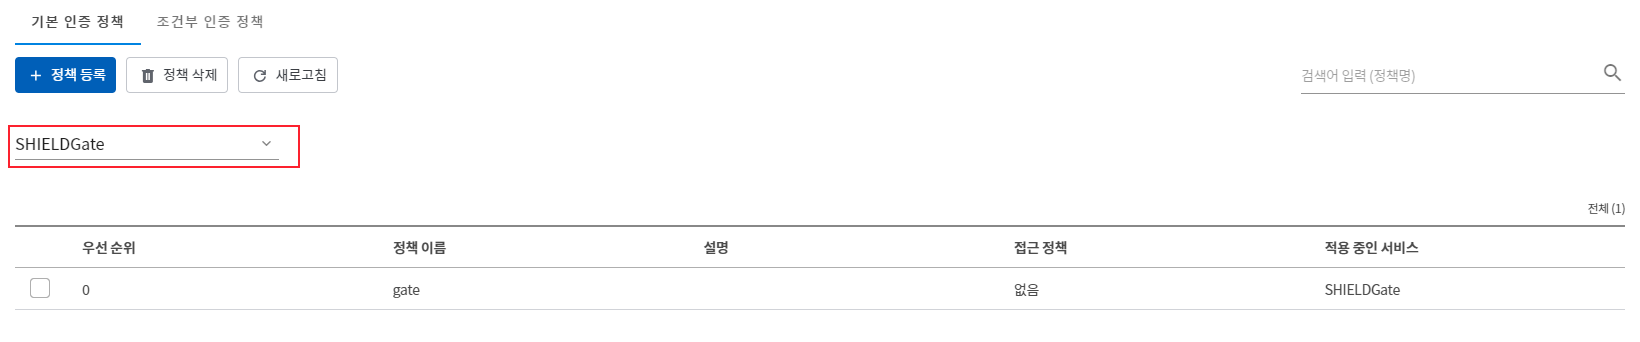
- After specifying the service you want to query, you can change the priority of the policy through drag and drop. (Priority changes are not possible during a full query.)
- You can enter the policy name in the search box at the top right to search.
Registration of Authentication Policy
- top
정책 등록You can add a policy by clicking the button. - Basic Authentication Policy
- You can allow or block access for specific users for each service.
- Enter policy name (required), description (optional), service (required), members (required), access policy (required).
- Enter the services and members to which the authentication policy will be applied.
- You can add users and groups registered in the user and group menu to the members.
- Select an access policy to choose whether to allow or block access.
- If you specify "Access Blocked", access will be blocked.
- If you specify "Allow Access," access will be granted, and you can select additional authentication methods.
- OTP Authentication: In addition to ID and password authentication, you must perform OTP authentication to access.
- Email verification: In addition to ID and password authentication, you must complete email verification to access.
- Not in use: You can access with just ID and password authentication.
- Enter the services and members to which the authentication policy will be applied.
- After completing the settings
추가Click the button.
- Conditional Access Policy
- You can allow or block access for specific users for each service and apply conditions.
- Conditional authentication policies are applied only when conditions are met. If the conditions are not met, the policy does not apply regardless of the access policy (allow or block).
- (Example) If you set the location (IP) condition to 40.60.120.1 - 40.60.120.245 and create an "Allow Access" policy, the policy will not apply to IPs outside the range, and login will proceed as normal.
- Enter policy name (required), description (optional), service (required), conditions (required), members (required), access policy (required).
- Enter the services and members to which the authentication policy will be applied.
- You can add users and groups registered in the user and group menu to the members.
- After selecting the service to which the policy will be applied, choose the conditions.
- condition is
조건 항목The list of conditions registered for the corresponding service will be displayed in the menu.
(Example) If you select the SHIELDrive service,조건 항목The list of conditions created by specifying SHIELDrive in the menu is displayed. - You can specify multiple conditions and choose between AND and OR methods.
- AND: The policy applies only if all conditions are met simultaneously.
- OR: The policy applies if at least one of the multiple conditions is met.
- condition is
- Select an access policy to choose whether to allow or block access.
- If you specify "Access Blocked", access will be blocked.
- If you specify "Allow Access," access will be granted, and you can select additional authentication methods.
- OTP Authentication: In addition to ID and password authentication, you must perform OTP authentication to access.
- Email verification: In addition to ID and password authentication, you must complete email verification to access.
- Not in use: You can access with just ID and password authentication.
- Enter the services and members to which the authentication policy will be applied.
- After completing the settings
추가Click the button.
info
To allow access only from a specific IP range
Set up one "Access Denied" conditional authentication policy based on allowed ranges.
조건 항목Create a location (IP) condition in the menu, and enter the remaining range excluding the allowed range.
- (example) 40.60.120.1 - 40.60.120.245 only allowed: 0.0.0.0 - 40.60.120.0, 40.60.120.246 - 255.255.255.255
- Specify the conditions, members, and "access block" for the conditional access policy.
- If the basic authentication policy "Access Denied" is applied to the same members, users within the range will also be blocked, so it is not used together.
- If the member includes an administrator account, administrators cannot log in from outside the range.
Authentication Policy Details/Edit
- You can click on the policy you want to check for detailed information.
- You can check the name, description, services applying the policy, set conditions, members, and configured access policies.
- You can click the edit icon at the top of the detail page to modify the condition information.
Delete Authentication Policy
- Select the policy you want to delete and click the delete policy button at the top to delete it.